Microsoft Details NeedyMantis Post-Compromise Malware Family
Microsoft Threat Intelligence has identified NeedyMantis, a modular post-compromise malware framework used in targeted intrusions. It combines custom loaders, encrypted archives, and extensible components to maintain long-term access.
 Microsoft
 Threat Intelligence identified NeedyMantis, a modular post-compromise malware framework used in targeted intrusions.
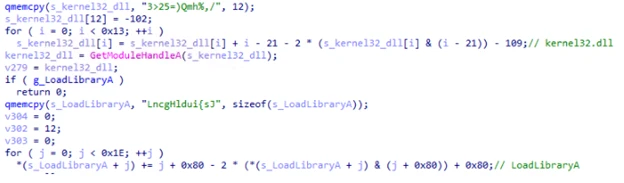
According to Microsoft, the framework combines custom loaders, encrypted archives, and extensible components.
The company said these elements are designed to maintain long-term access and support follow-on operations.
The information appeared in a post on the Microsoft Security Blog titled "NeedyMantis: Unpacking a post-compromise malware family used in targeted operations".
Original publication date
September 28, 2026